Breaking the silo
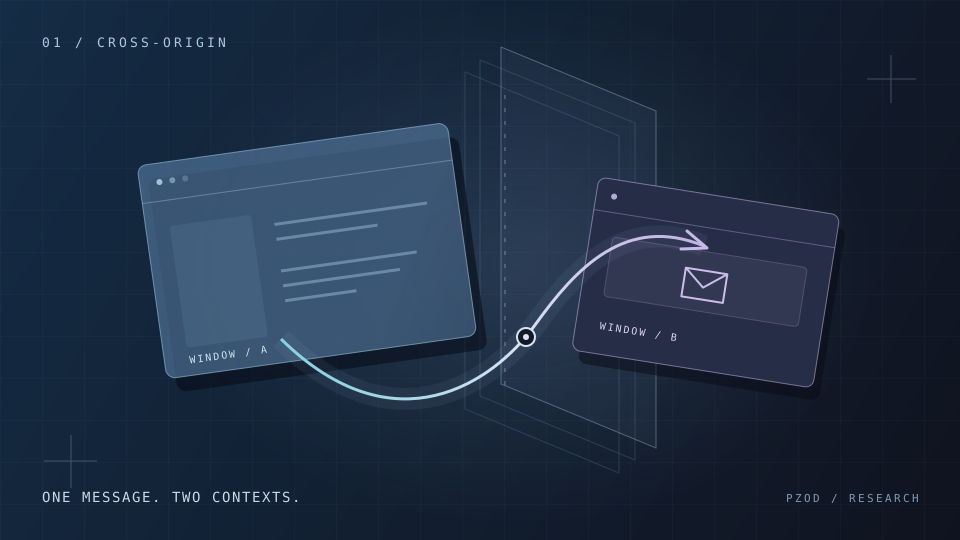
Cross-origin communication, trust boundaries, and the anatomy of postMessage XSS.
I’m an associate pentester and security consultant in Sydney. I write about the vulnerabilities I investigate, the tools I build, and what I learn along the way.
Web security · Active Directory · Offensive research
Research, technical writeups, and the details behind the finding. These are a few places to start.
Explore all researchCross-origin communication, trust boundaries, and the anatomy of postMessage XSS.
A collection of notes on endpoint visibility and red team techniques.
Exploring injection patterns, filters, and modern application attack surfaces.
Following a server-side request beyond the application's trust boundary.
A domain can look trusted and still belong to someone else. Change the comparison, send a message, and see exactly where the check fails.
Follow the full attack pathChoose an origin. Change the check.
Watch what crosses the boundary.
https://trusted.exampleCan a lookalike cross the boundary?
Small utilities for inspecting tokens, following messages, and working through an idea.
Browse the toolsInspect token structure and experiment with claims in a browser workspace.
Open workspaceExplore window messaging with a target frame and communication log.
Open workspaceFrom OSCP notes to technical presentations. The things that helped something click.
All field notesResearch, collaboration, or a good technical conversation.
Let’s talk